This article contains affiliate links. Purchases through these links may earn us a commission at no extra cost to you.
This Vibe App Scanner review starts with a question that matters more than any product: is your vibe-coded app safe to put in front of users? Research says probably not by default. Below you will find what the scanner checks, what its first buyers found, where it gets things wrong, and a checklist you can run before paying anyone.
Based on the Vibe App Scanner website and its AppSumo listing with the first three verified reviews. For the security context we used independent research (SusVibes, Veracode, Georgia Tech), the write-up of the Lovable RLS vulnerability, and Supabase’s documentation. Last updated: September 2026.
Vibe App Scanner review verdict (2026)
Vibe App Scanner is a young, focused tool from two security professionals. It tests your live app from the outside, ranks what it finds and writes the fix for your AI coding tool. Early buyers like the fixes and the founder’s support. One careful buyer also caught false positives, so read every finding before you apply it. See the current AppSumo deal.
Key Takeaways
- Vibe App Scanner says it runs 150+ checks against a live URL, including exposed API keys, database permissions and login flows. (vibeappscanner.com [1])
- The AppSumo deal costs $49 once for 15 scans a month; the regular Go plan is $19 a month. (AppSumo)
- Veracode found security flaws in 45% of AI-generated code across more than 100 language models. (Veracode)
- One Lovable vulnerability exposed data in 170 of 1,645 apps analyzed, including emails, phone numbers and payment details. (CVE-2025-48757)
- Only three buyers have reviewed it so far (4.67/5); one reported wrong stack detection and a misleading fix, which the founder confirmed. (AppSumo reviews [3])
1Is vibe coding safe? What the research says
Often not, at least not by default. Independent studies find that AI coding tools produce working code far more often than secure code. The typical failures are simple. Database tables anyone can read, secret keys shipped to the browser, and APIs that check you are logged in but not what you may see.
The SusVibes benchmark from Carnegie Mellon’s Lei Li Lab tested 12 agent setups on 186 real-world coding tasks. In the authors’ words, all agents performed poorly on software security. Adding vulnerability hints to the prompt did not fix it (arXiv 2512.03262). Georgia Tech’s Vibe Security Radar confirmed 74 real vulnerabilities (CVEs) traced to AI coding tools between mid-2025 and March 2026 (Georgia Tech).
How to secure a Supabase app: start with RLS
Many AI-built apps run on Supabase. Its documentation is blunt: a table in an exposed schema without Row Level Security is readable and writable by any role that has access. It also warns that the secret (service role) key bypasses those rules and must never be used in the browser (Supabase docs). The public “anon” key, by contrast, is meant to be visible. The Vibe App Scanner founders say plenty of generic scanners confuse the two, and their tool checks for both secret keys in your JavaScript and weak RLS rules.
We saw the human side of this in the Huntarr security incident. Our Brows3 review covers S3 buckets, storage that leaks the same way when permissions are left open.
2What is Vibe App Scanner?
Vibe App Scanner is a hosted security scanner for apps built with AI tools. You paste the URL of your live app, it detects your stack and runs over 150 checks. Every finding comes with a severity, an explanation, the raw evidence and a fix you can paste into Lovable, Cursor or Claude Code.
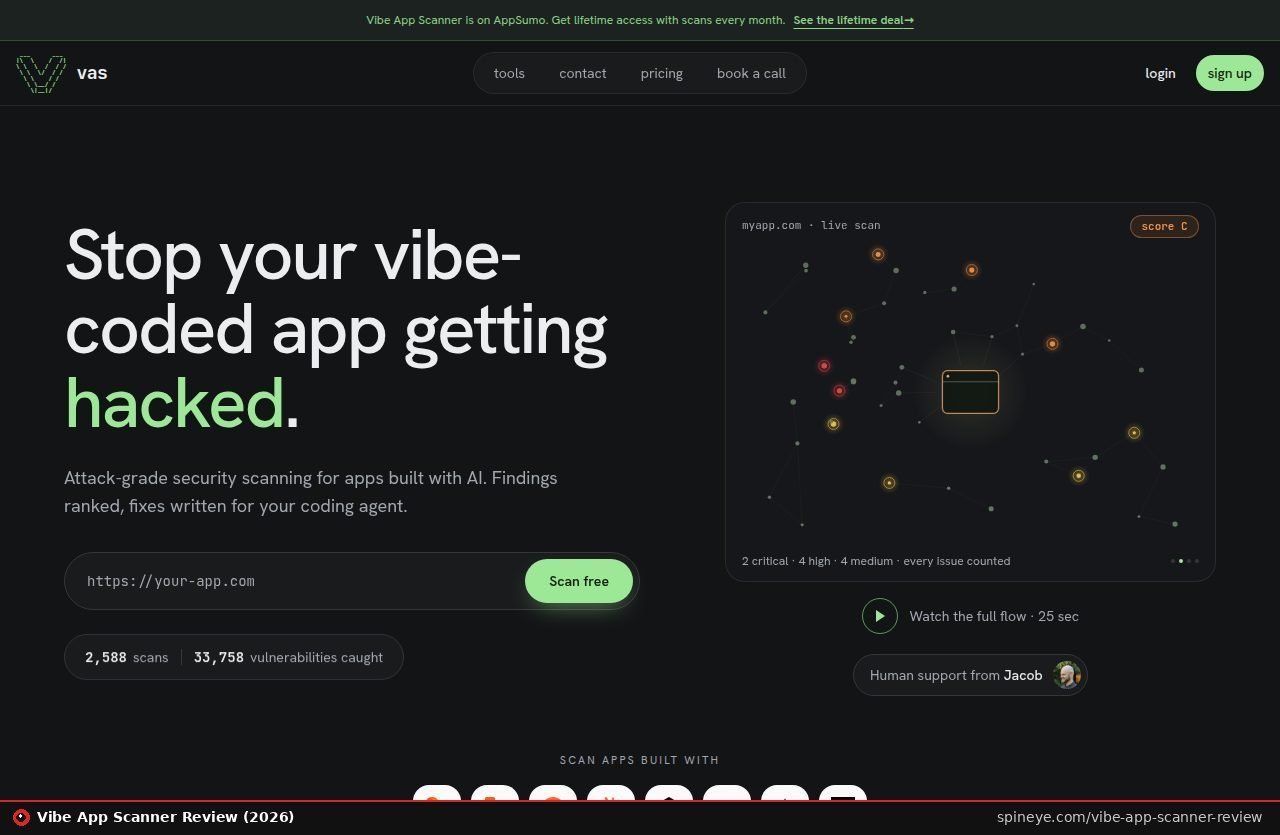
The maker lists eight check areas. The security ones are vulnerabilities such as SQL injection and broken access control, database and login rules, secrets in your JavaScript bundles, and headers such as CSP and CORS. The others cover infrastructure, SEO and AI-search readiness, accessibility and compliance, and performance (vibeappscanner.com [1]).
You can add test login details so it also checks pages behind a login. Findings reach your AI tool by copy-paste on every plan, and through MCP, an API or SARIF and raw JSON output on higher plans. Then you scan again to confirm the fix. On the lifetime deal, MCP, weekly automated scans and breach monitoring start at Tier 2, and API access comes with Tier 3.
The company was founded in November 2025 in Ontario, Canada. Its two founders say they spent almost two decades in cybersecurity. They built the scanner after audits of apps made with Lovable, Base44, Replit and Claude kept turning up the same holes (AppSumo founder post). The same team runs Spring Code, which sells manual audits.
The SEO and AI-search checks are a bonus rather than the core. For that topic, our Nuwtonic review and Honeylog review go deeper on that side.
3Vibe-coded app security checklist
Before you pay for any scanner, check nine basics yourself. Keep secret keys out of the browser and put owner-based rules on every table. Check permissions in every API and rate-limit logins. Hide config files, set security headers, patch dependencies, authenticate your email, and get a human review for sensitive data.
Some of these fixes live at the hosting level rather than in your code. If you are planning a move off basic shared hosting, our shared-to-cloud hosting migration guide walks through it.
4What do users say about Vibe App Scanner?
There are only three AppSumo reviews so far, averaging 4.67 out of 5. Buyers praise the copy-paste fixes and a very responsive founder. The most useful review is the four-star (four-taco) one: the report misidentified the hosting and suggested an unnecessary security change, which the founder confirmed and promised to fix.
The five-taco reviews are positive but need context. One comes from a paid AppSumo product tester who received the tool for free, as the review itself discloses. He says scanning and fixes worked well, and that the team added PDF reports and a REST API after his feedback. He adds that he would still want a proper security review for an app handling sensitive data. Another buyer praises the founder’s detailed pre-sale answers and says the scan caught form labels that were not linked to their fields (AppSumo reviews [3]).
“I wouldn’t trust the scan reports 100% at the current state.”— dokgu, four-taco review, AppSumo [3], September 2026
That reviewer’s app is a Next.js app in Docker, not hosted on Vercel, yet the report said Vercel. It also advised a CSP frame-src rule for YouTube embeds the app does not have. Following that advice blindly would have added attack surface. The founder reproduced both problems within a day and said he would correct the detection rules. That response is a good sign; the finding itself is a reminder to read the evidence before you paste a fix.
On YouTube, the most visible test is a creator scanning his own to-do app with a planted flaw. Its description says it is sponsored by AppSumo, so treat it as a demo rather than an independent review. His written test, published 23 September 2026, adds one limit worth knowing. The AppSumo deal does not include deep scans, which log in and crawl pages behind your login (source [8]). The maker lists those on its own Pro subscription. In developer forums, launch threads for vibe-code scanners draw the same two objections: worries about handing over your code, and “why not use open-source tools?”. Vibe App Scanner’s answer is that it tests the live app from outside, without access to your code.
5How much does Vibe App Scanner cost in 2026?
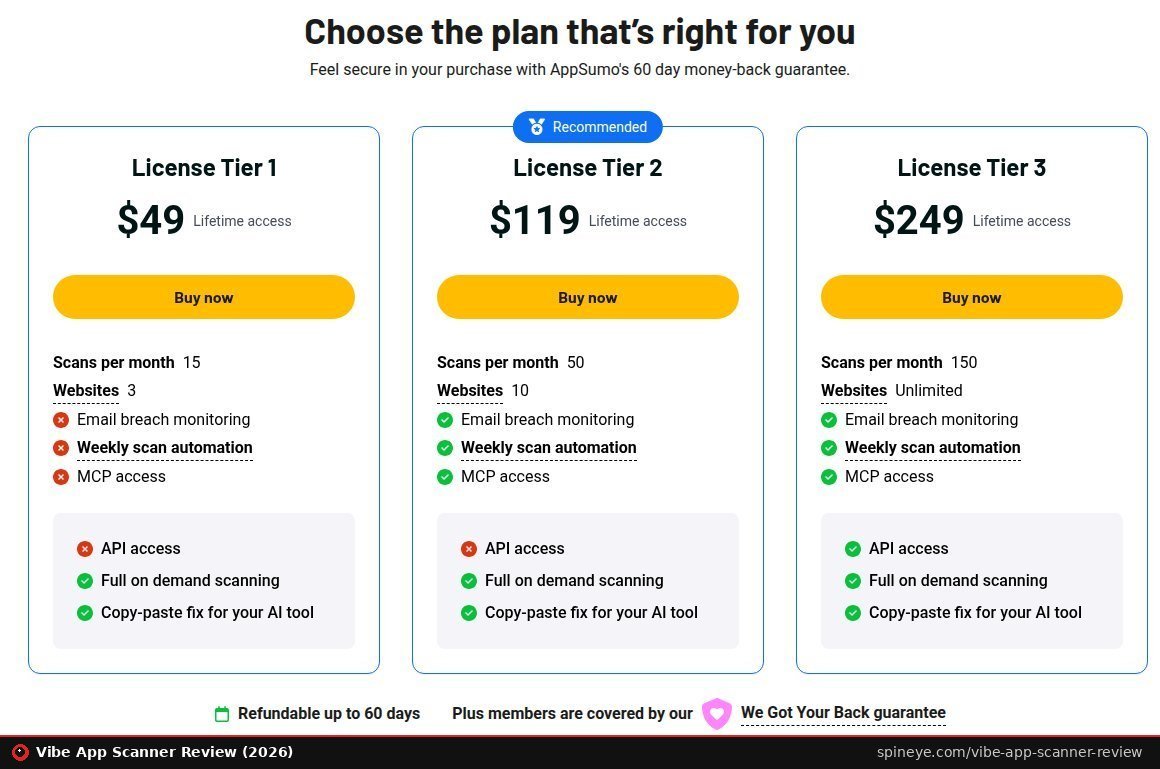
On AppSumo, Vibe App Scanner costs $49, $119 or $249 once for 15, 50 or 150 scans a month, with a 60-day refund. Tier 1 covers on-demand scans and fixes; MCP and weekly automation start at Tier 2. The regular plans are Go at $19 and Pro at $39 a month.
| Plan | Price | Scans / month | Sites / projects | MCP / weekly scans / API |
|---|---|---|---|---|
| AppSumo Tier 1 | $49 once (was $240) | 15 | 3 | – / – / – |
| AppSumo Tier 2 | $119 once (was $350) | 50 | 10 | ✓ / ✓ / – |
| AppSumo Tier 3 | $249 once (was $480) | 150 | Unlimited | ✓ / ✓ / ✓ |
| Go (subscription) | $19 / month | 20 | 3 | On-demand re-scans |
| Pro (subscription) | $39 / month | 150 | 10 | Weekly deep scans + monitoring |
Sources: AppSumo and vibeappscanner.com [1], checked 26 September 2026. Tier 1 receives future Go updates, Tiers 2–3 future Pro updates. The first scan on the website is free but shows only your score and issue counts.
The deal terms add one caveat we have seen on other lifetime deals: access to future AI models “may require an add on”. As with our Vexp review, a young company is part of what you are buying, so use the 60-day refund window to scan your real apps.
Tier 1 is $49 once for 15 on-demand scans a month on up to 3 websites. Tier 2 adds MCP and weekly automated scans. Both come with a 60-day refund.
See the Vibe App Scanner deal
6Vibe App Scanner vs free scanners and manual audits
Free scanners check what any visitor can see, such as headers and exposed files. Vibe App Scanner also scans from outside, but says it probes database rules, logins and APIs. It can test pages behind a login and writes fixes for your AI tool. A manual audit by a security professional remains the standard for apps with sensitive data.
Want monitoring of headers, TLS and DNS instead of app-level leaks? Our Barrion review compares Barrion with Vibe App Scanner side by side.
| Option | Cost | What it checks | Best for |
|---|---|---|---|
| Free visitor-level scanners | Free | Headers, TLS, publicly visible files | A first sanity check |
| Vibe App Scanner | $49 once / $19 mo | 150+ checks incl. database rules, auth, secrets, APIs | Repeat checks after each deploy |
| Manual security audit | Quote-based | Code and logic review by a person | Apps with sensitive data |
Sources: vibeappscanner.com [1]; free scanner descriptions from their own pages, checked 26 September 2026.
A free scanner such as VibeZero says plainly that it checks what a visitor can see and marks what it could not confirm. That honesty is useful, and a good reason to start there. The step up to Vibe App Scanner makes sense once you deploy often and want the fixes written for you. The paid tester makes the key point himself, and the founder agreed: for an app with sensitive data, you still want a proper security review. That is the same small-tool trade-off we keep meeting in our hidden-gem software research.
7Vibe App Scanner pros and cons
Its strengths are checks built for AI-generated stacks, fixes written for your coding agent, re-scans to confirm, and an unusually responsive founding team with security backgrounds. Its weaknesses are very few reviews, reported false positives, a paywall after the free score, and a company that is less than a year old.
Pros
- 150+ checks tuned to Supabase, Firebase and AI-built stacks (source [1])
- Copy-paste fixes on every plan; MCP and API on higher tiers (source)
- Raw evidence behind each finding (source)
- Can test pages behind a login (source)
- Founders with a security background who respond fast to reported issues (source [3])
- Also flags SEO, accessibility and email issues (source [1])
Cons
- Only three AppSumo reviews, one from a paid tester (source [3])
- Reported wrong stack detection and a misleading fix (source [3])
- Free scan shows only the score and issue counts (source [1])
- Interface described as basic; passed checks hard to read (source [3])
- Tier 1 has no MCP, weekly scans or API, and fewer scans than Go (source)
- No deep scans behind a login in the AppSumo tiers (source [8])
- Future AI models may need an add-on (source)
- Founded November 2025; no track record yet (source)
8Who should buy Vibe App Scanner?
It suits solo founders, small agencies and vibe coders who ship on Supabase or Firebase without a security person. They get a quick, repeatable check with fixes their AI tool can apply. It is not a substitute for a professional audit on apps that store sensitive personal or financial data.
In short, this Vibe App Scanner review finds a real, well-documented problem and a product that tackles it sensibly: from the outside, with evidence and ready-made fixes. It is also very new. Three reviews are not a track record, and one of them caught mistakes a beginner might have applied without thinking. Run the checklist above first. If it leaves doubts, the $49 tier with a 60-day refund is a low-risk way to see the full findings on your own apps. If you work in Cursor or Claude Code, or run several client apps, Tier 2 is the sensible pick: it adds MCP, weekly scans and 10 websites.
Good fit: Lovable, Replit, Bolt, Cursor and Claude Code builders; agencies shipping small client apps; anyone who deploys weekly. Poor fit: regulated or high-risk apps that need a signed audit, and developers who already run their own security tooling. If you build with Claude, our Accordio review looks at a related question: how much access you should give AI tools that act on your data.
Tier 1 is $49 once. Tier 2 ($119) adds MCP and weekly scans, with 50 scans a month on 10 websites.
Get Vibe App Scanner on AppSumo
About this Vibe App Scanner review
- Basis: the Vibe App Scanner website and AppSumo listing, its three verified AppSumo reviews, and the founders’ own post.
- Research: figures taken from the original sources (SusVibes, Veracode, Georgia Tech, CVE-2025-48757, Supabase docs). Where the maker’s site cites an earlier or later version of a figure, we use the original source.
- Checklist: each item is tied to Supabase’s documentation, the scanner’s published check categories, or reviewer and founder advice.
- Checked: all prices and ratings on 26 September 2026.
- No star rating: the product is under a year old, so we lay out the evidence and let you weigh it. How we review.
Frequently asked questions
Is vibe coding safe?
Not by default. In the SusVibes benchmark only 11.8% of the solutions from SWE-Agent with Claude 4 Sonnet were secure, and Veracode found flaws in 45% of AI-generated code. Checking database rules, secrets and permissions before launch closes the most common gaps.
Is Vibe App Scanner legit?
Yes. It is built by two founders with a cybersecurity background, has a free first scan and a 60-day refund on AppSumo. It is very new, with only three reviews so far.
Does Vibe App Scanner need my source code?
No. It scans your live app by URL from the outside. You can optionally add test login details to check pages behind a login.
Can I trust every finding?
Not blindly. One buyer reported wrong hosting detection and an unnecessary security suggestion, which the founder confirmed. Read the evidence before applying a fix.
How do I secure a Supabase app before launch?
Enable Row Level Security on every table in an exposed schema, with owner-based policies. Never ship the secret (service role) key to the browser. Check that your APIs verify what each user may access.
How much is the Vibe App Scanner lifetime deal?
On AppSumo, $49 for Tier 1, $119 for Tier 2 and $249 for Tier 3, each a one-off payment with a 60-day refund. Deep scans that log in and crawl behind your login are not part of the deal.
Sources
- Vibe App Scanner — homepage, checks and pricing. vibeappscanner.com
- AppSumo — Vibe App Scanner listing, plans and founder post (checked 26 Sep 2026). link
- AppSumo — Vibe App Scanner reviews (3). link
- Zhao et al. — “Is Vibe Coding Safe? Benchmarking Vulnerability of Agent-Generated Code in Real-World Tasks” (SusVibes). arXiv 2512.03262
- Veracode — AI-generated code security risks (2025 GenAI Code Security Report). link
- Georgia Tech — “Bad Vibes: AI-Generated Code is Vulnerable, Researchers Warn” (13 Apr 2026). link
- Matt Palmer — Statement on CVE-2025-48757 (Lovable RLS). link
- Dave Swift — “Vibe App Scanner: What Its AppSumo Quick Scan Found” (23 Sep 2026, sponsored by AppSumo). daveswift.com/vibe-app-scanner
- Supabase — Row Level Security documentation. link
AI assistance was used for research and drafting; every fact was checked against the listed sources. Prices and figures checked 26 September 2026.